The full anatomy of a phishing site,
one URL at a time.
ZeroPhish renders the page, runs twelve detection signals against the DOM, certificate chain, brand fingerprint and threat feeds, and returns a typed verdict. Built for security teams and product engineers.
Phishing detected
| URL | hxxps://klugeignungswerk[.]com/ | |
| Host | klugeignungswerk[.]com | |
| Brand | Klug Eignungswerk | |
| Screenshot | https://cdn.zerophish.ai/8c2af3c4-8256-4a4f-b70e-e337ceaa189b.jpg | |
| Scan ID | 4034d85e-887d-48ae-839b-33d5fa3a699f |
| Host | klugeignungswerk.com |
| Registered domain | klugeignungswerk.com |
| Scheme | https |
| Content length | 222386 B |
| HTTP | 200 · text/html |
| DMARC policy | none |
| SPF policy | none |
| MX records | none |
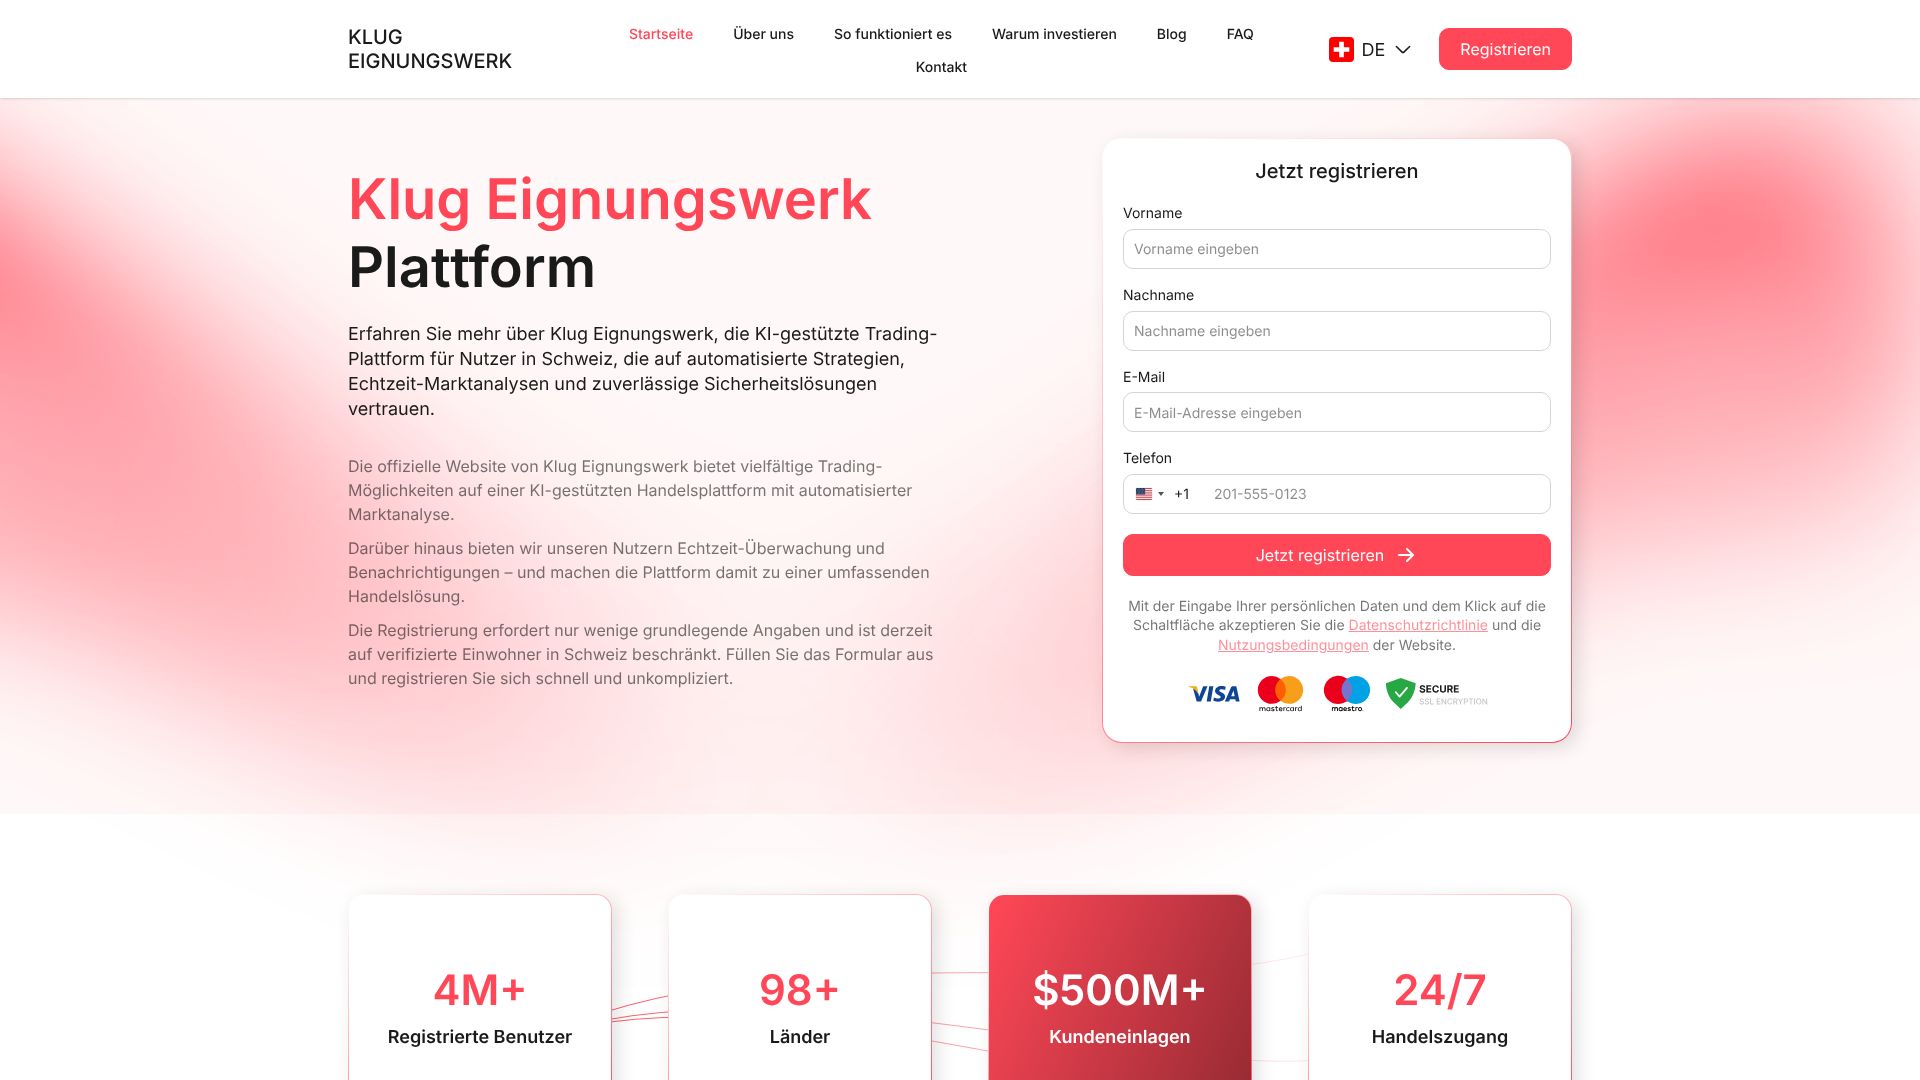
The page presents itself as the “offizielle Website von Klug Eignungswerk” and a “KI-gestützte Trading-Plattform” with a “Jetzt registrieren” flow. It contains a credential/lead collection form posting to “/api/send” with fields for name, email, and phone, which is a common setup for harvesting user data or funneling victims to later account/financial steps.
Key suspicious signals include: (1) aggressive onboarding to a trading platform with promises of security/transparency but without verifiable brand/domain ownership signals beyond self-claims, and (2) a data-collection form immediately presented as the primary action, plus marketing claims like “4M+ registrierte Benutzer” and “Kundeneinlagen” that can be used to create legitimacy. The URL is not a lookalike of a major brand (so no clear “favicon impersonation” or PayPal-style mismatch), but the combination of trading-themed urgency and immediate form submission on an unfamiliar domain still warrants a phishing classification with low confidence.
Conclusion: phishing (or scam-likely) rather than clearly legitimate, mainly due to the presence of a lead/credential collection form within a high-risk financial/trading context and insufficient independent verification from the provided content.